Prove Governance and Compliance

Move beyond checkbox security to provable defense. Flecks maps live detection coverage to fourteen frameworks including NIS2, DORA, ISO/IEC 27001:2022, SOC 2, PCI DSS 4.0, CMMC 2.0 and NIST 800-53, and exports assessor-ready evidence packs that separate what Flecks verifies from what you attest. We give leadership the forensic-grade evidence required to satisfy regulators, pass audits, and secure competitive cyber insurance rates.

Flecks is itself certified to ISO/IEC 27001:2022. The platform maps your coverage to ISO 27001 and thirteen other frameworks, and the company running it is audited against the same standard.
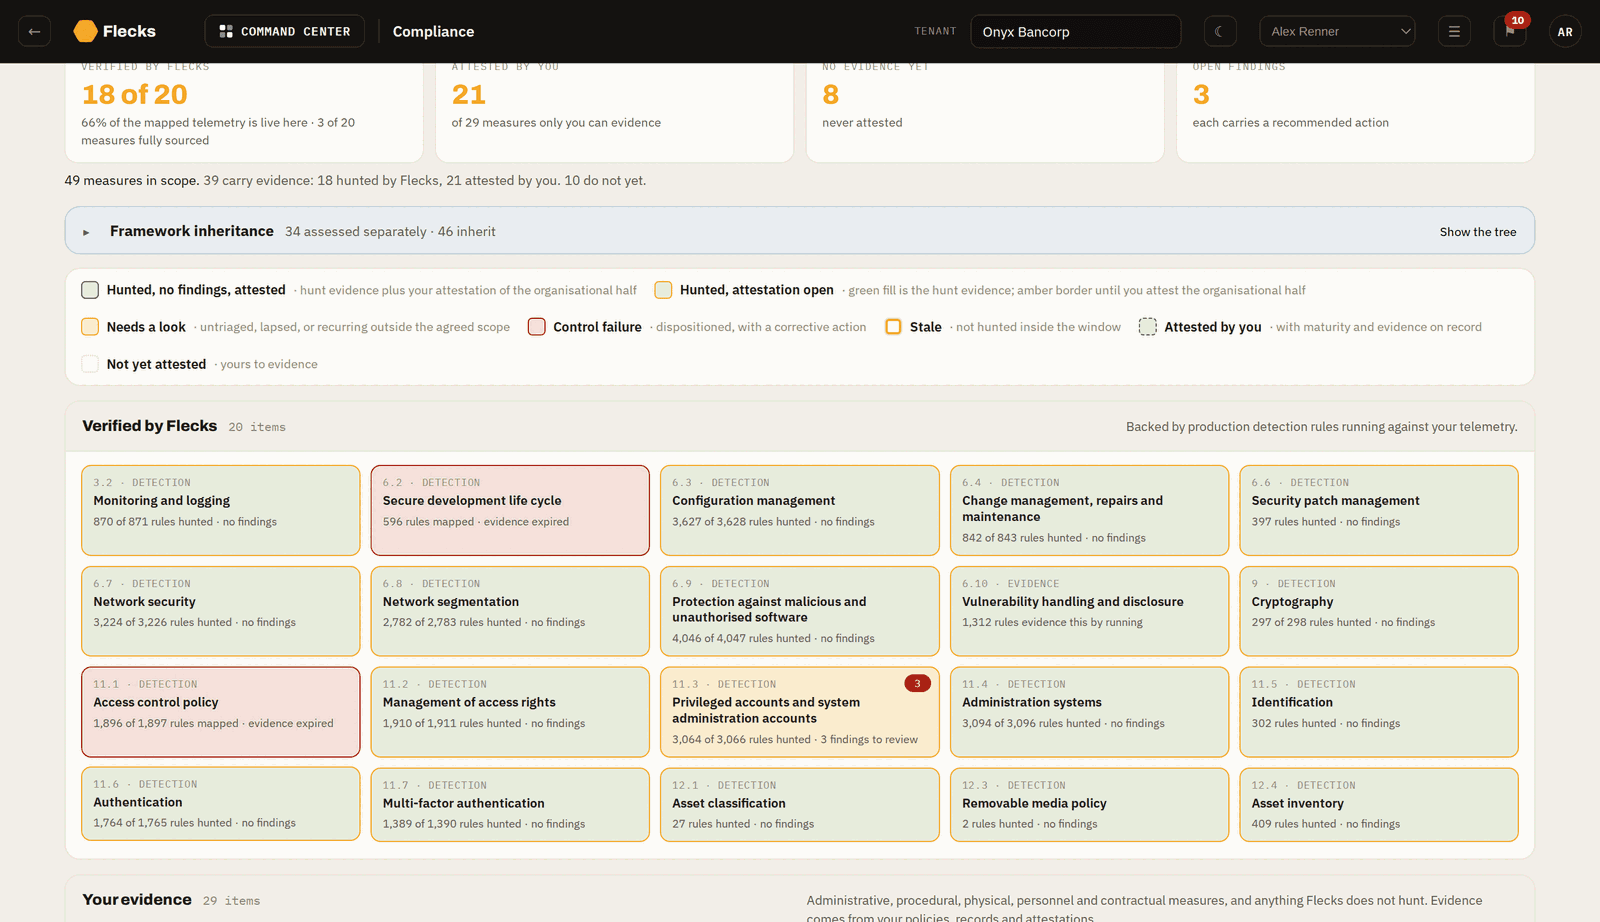
Defensible Governance: Verifiable Compliance and Risk Control

Regulatory failure leads to massive fines and reputational damage. Flecks automates control verification, providing continuous evidence of proactive threat identification and incident response compliance to satisfy auditors, lower insurance premiums, and protect executive liability.

Map to Regulations
Audit-Ready Evidence
Lower Insurance Risk
Explore the Outcomes

Our Strategic Approach

Map to Regulations

Regulatory Alignment: Automated Framework Mapping

Fourteen Frameworks, Natively Rendered Every control is presented in its own framework's structure, not a generic checklist: NIS2 by Annex measure, ISO/IEC 27001:2022 by Annex A control, plus DORA, SOC 2, PCI DSS 4.0, CMMC 2.0, NIST 800-53 r5, NIST CSF 2.0, CIS v8.1, HIPAA, GDPR, CISA Zero Trust and ACSC Essential Eight.
Honest Scope, Stated Up Front Coverage is split into what Flecks verifies from your telemetry and what only you can evidence through policy and attestation. A pack that omits what a security platform cannot observe reads as complete when it is partial.
Enforce Data Sovereignty Enforce data residency and citizenship requirements automatically, ensuring global operations respect local sovereignty and strict international privacy laws.
Audit-Ready Evidence

Continuous Validation: Audit-Ready Evidence

Immutable Audit Trails Maintain an immutable historical record of all hunting and remediation actions, creating an unassailable audit trail for external examiners.
Reduce Audit Costs Generate reports that prove controls are active, reducing the billable hours spent preparing for external audits.
Evidence of Absence, Not Assumption When a control is hunted and nothing is found, that is a defensible statement about the scope tested: the measure was tested, the tests did not fire, and the rules behind the claim are listed. It is evidence that the control is effective, not silence mistaken for safety.
Lower Insurance Risk

Financial Protection: Lowering Insurance Risk

Reduce Premium Costs Demonstrate a mature, proactive security posture to underwriters, aiding in the negotiation of lower cyber insurance premiums.
Ensure Insurability Satisfy increasingly strict carrier requirements for ransomware protection and monitoring to ensure your organization remains insurable against catastrophic loss.
Expedite Claims Processing Expedite insurance claims processing by providing insurers with precise timelines and definitive proof of due diligence during an incident.

See our approach in action

Contact Sales
Offer for sectors

More from Flecks

Discover how Flecks can help your organization achieve its security goals across platforms, industries, and strategic outcomes.