

Answer the Regulator With Data
NIS2 and DORA ask what you actually do, not what your policy says. Flecks reports coverage measure by measure against the framework's own structure, backed by the detection rules that ran against your telemetry.
Turn threat hunting into audit evidence. Flecks maps live detection coverage to fourteen frameworks, tracks what only you can attest to, and exports a pack an assessor can work from.
NIS2 and DORA ask what you actually do, not what your policy says. Flecks reports coverage measure by measure against the framework's own structure, backed by the detection rules that ran against your telemetry.
The evidence pack is generated from the same data the platform hunts on. There is no separate reconciliation exercise, and no gap between what the security team reports and what the compliance team submits.
Assign frameworks per entity across a corporate group. Subsidiaries inherit from a parent or are assessed in their own right, and each gets its own report.
Every framework renders in its own structure, coverage is stated honestly, and attestations stay current across every entity in your group.
Every framework renders in its own structure rather than a generic control set. NIS2 by Annex measure, ISO/IEC 27001:2022 by Annex A control, and twelve more. Each control shows how many library rules hunted against it and what came back.
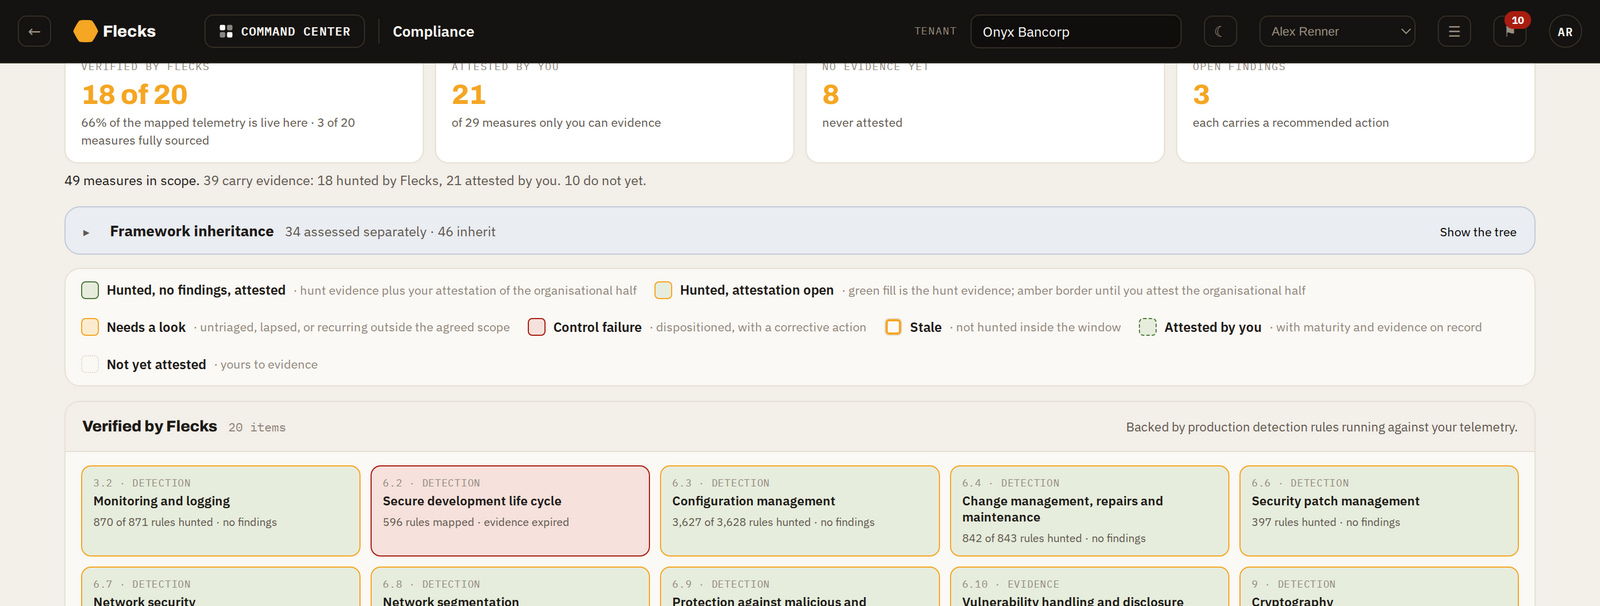
Product screenshot. Figures shown are from a demonstration environment.
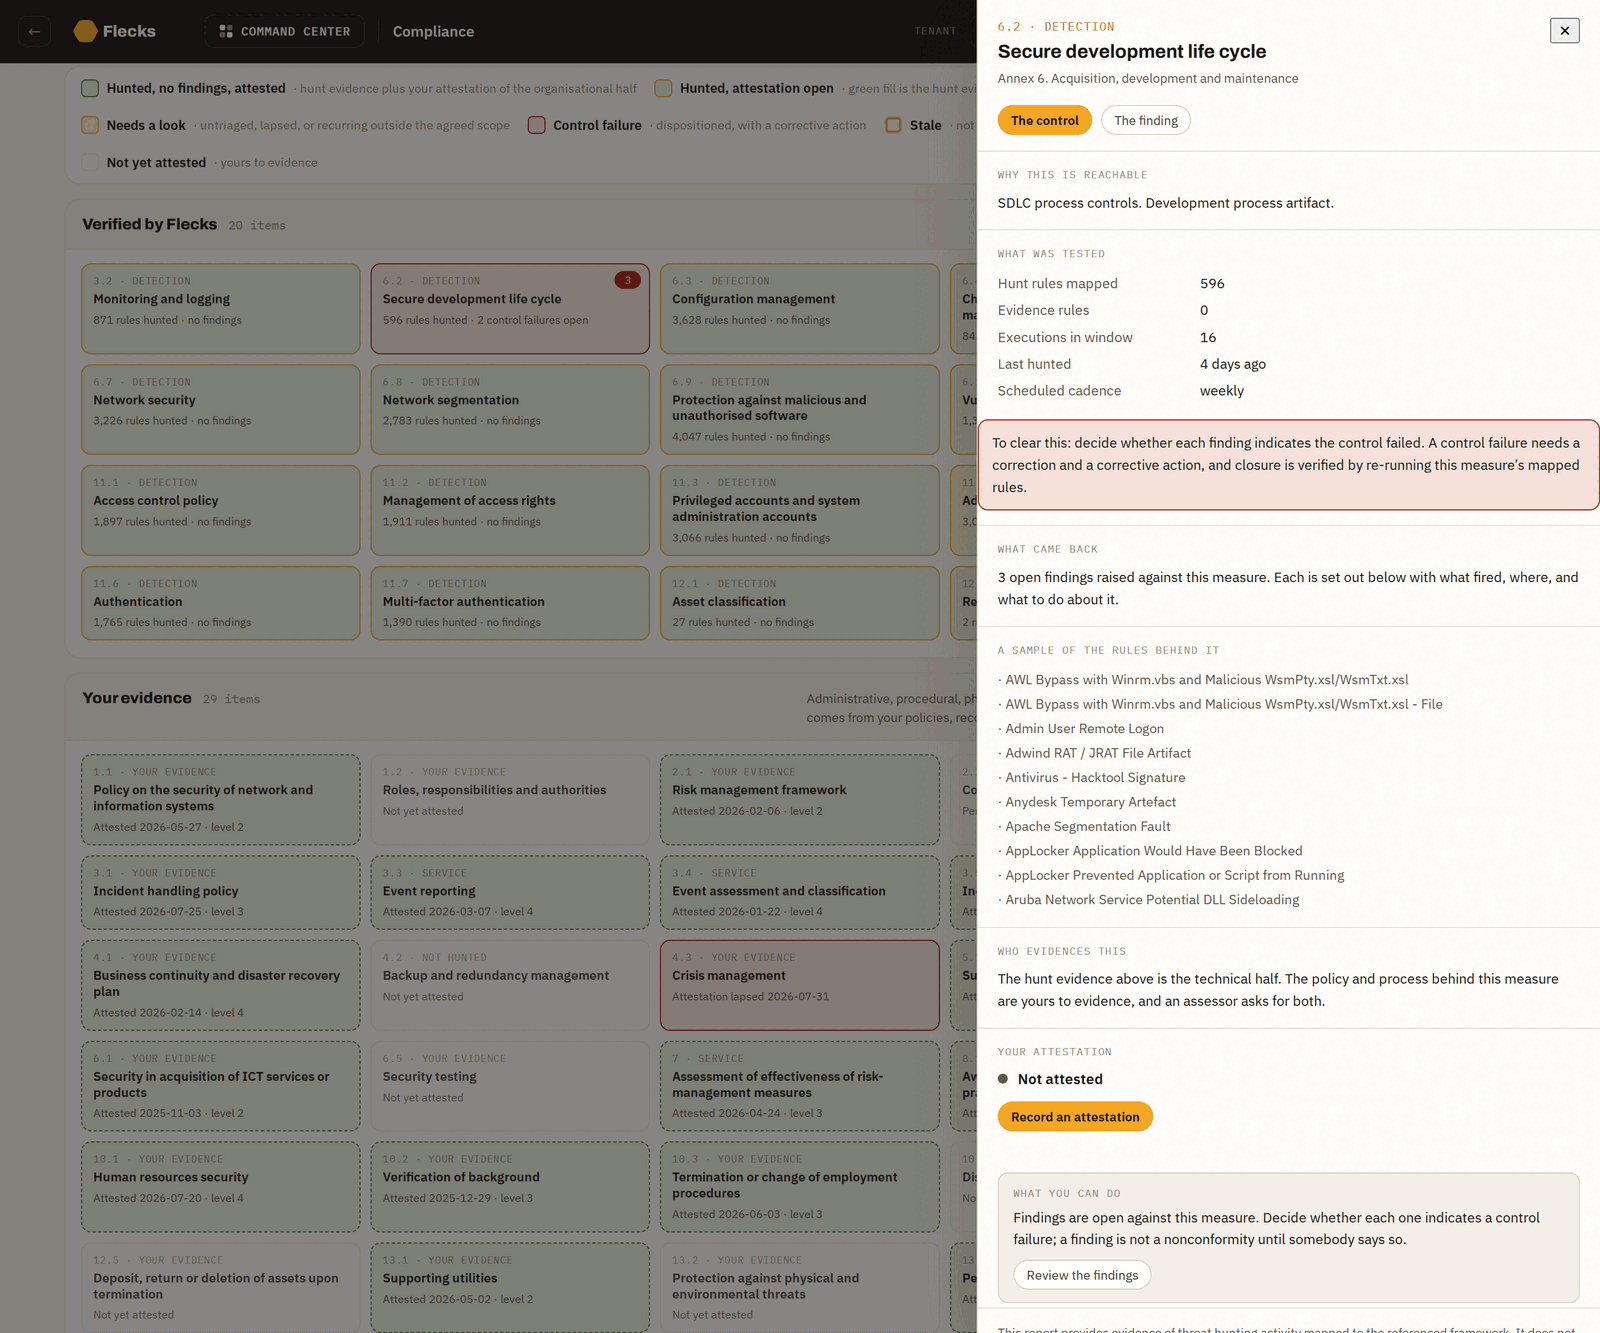
Product screenshot. Figures shown are from a demonstration environment.
When a control is hunted and nothing is found, Flecks says exactly that, names the rules that ran, and states the scope tested. Where evidence is stale or a schedule has lapsed, it says that too rather than reporting a pass.
Assign NIS2, DORA, ISO 27001, PCI DSS or CMMC per entity. Subsidiaries either inherit from a parent or are assessed separately and receive their own report. Residency and industry are first-class filters.
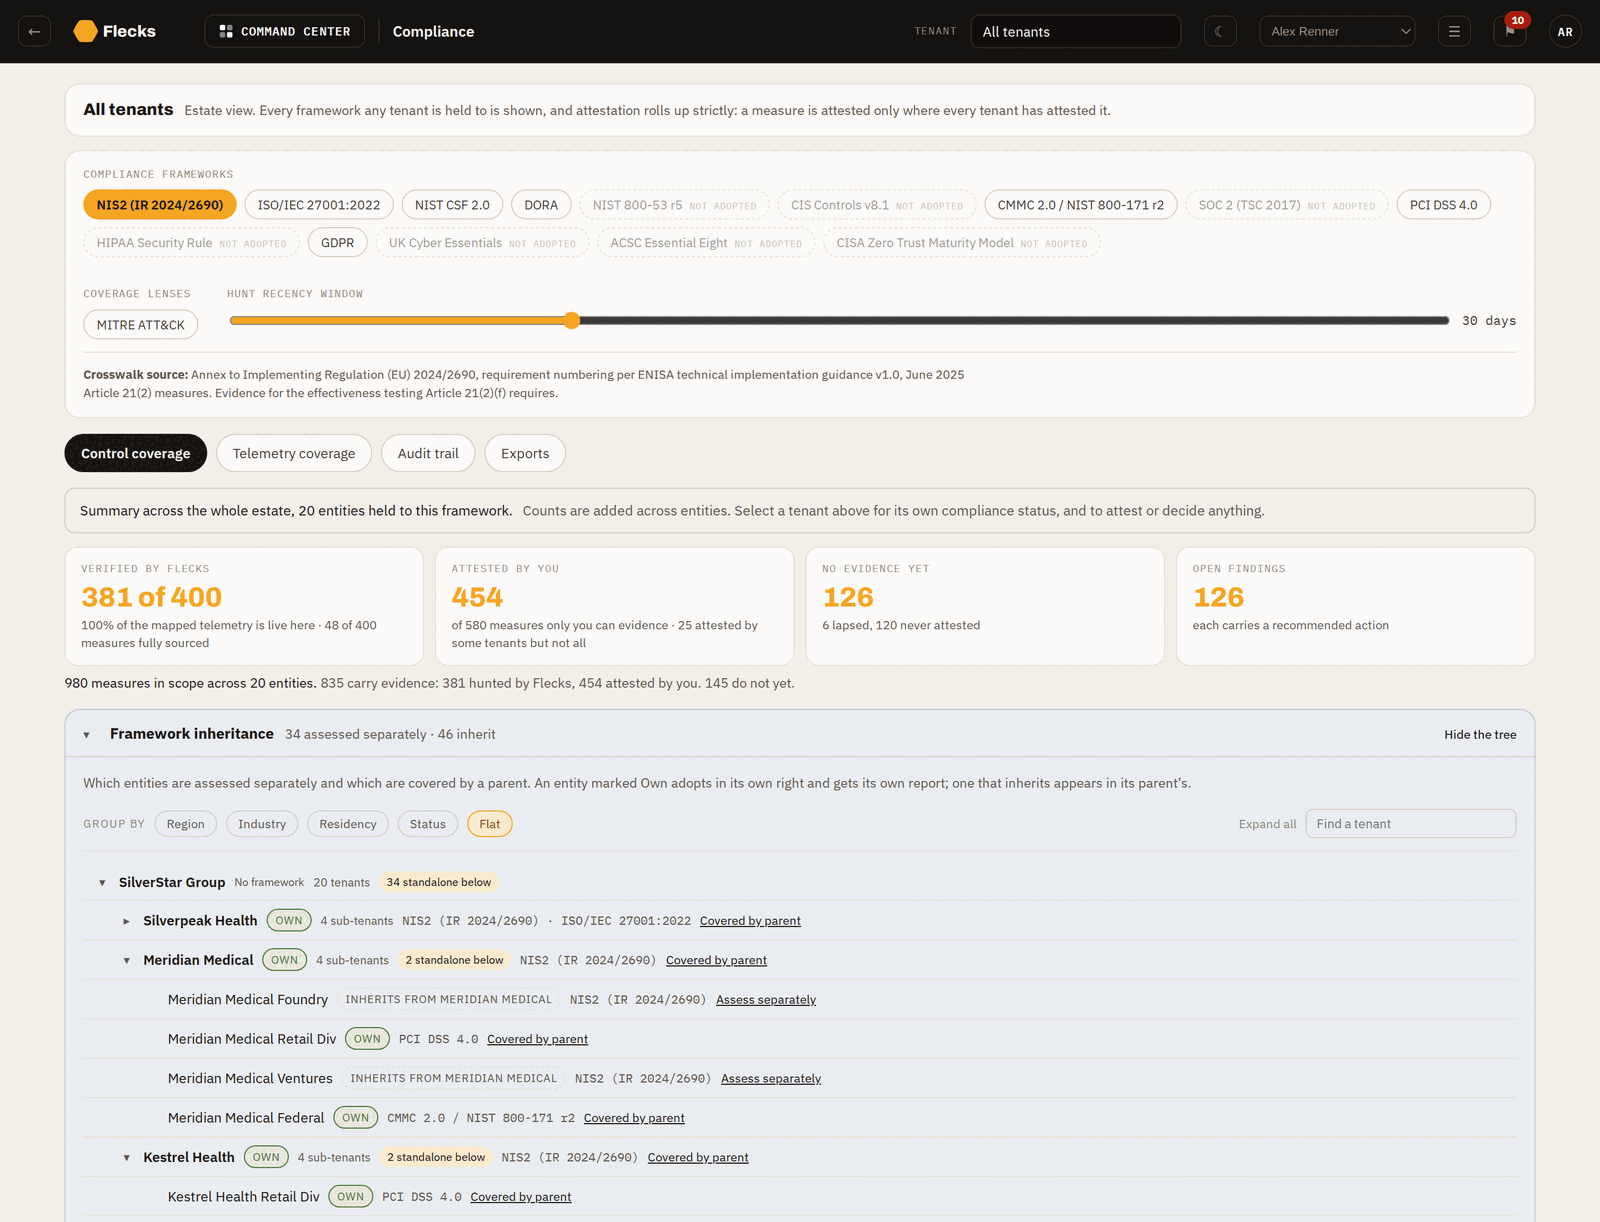
Product screenshot. Figures shown are from a demonstration environment.
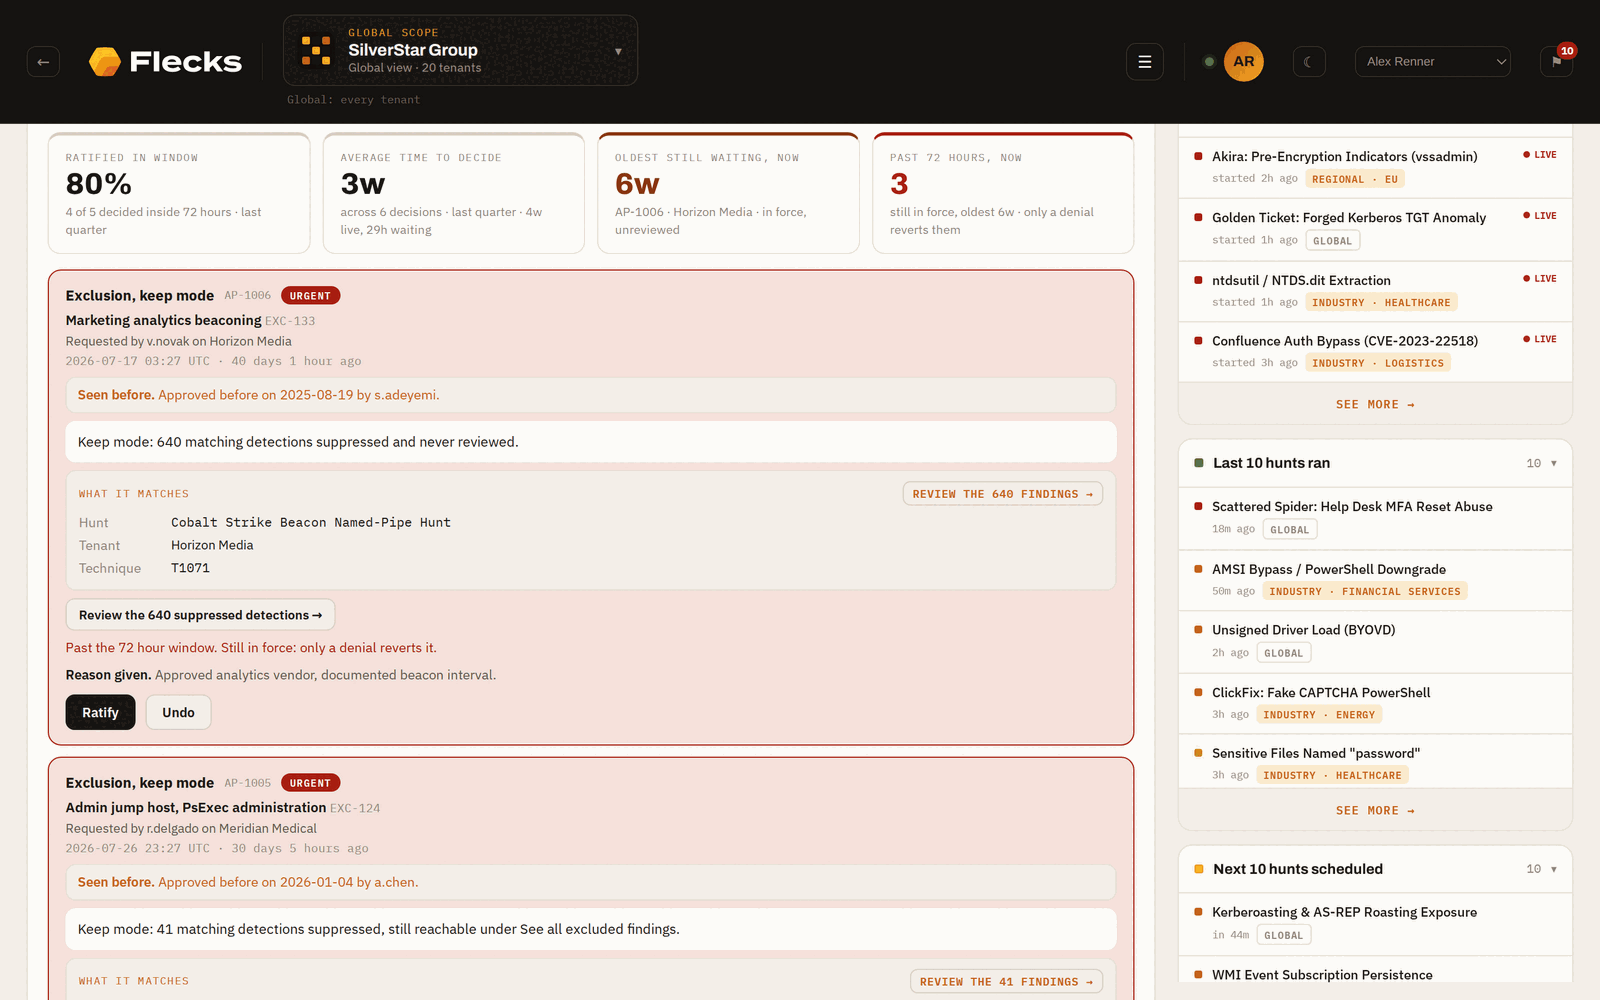
Product screenshot. Figures shown are from a demonstration environment.
Administrative and contractual measures no security tool can observe are carried explicitly as your evidence, with attestation dates, maturity levels and renewal tracking. A lapsed attestation reads as a gap in the pack, not as a silent pass.
Flecks is certified to ISO/IEC 27001:2022.
Discover how Flecks can help your organization achieve its security goals across platforms, industries, and strategic outcomes.


